Blog
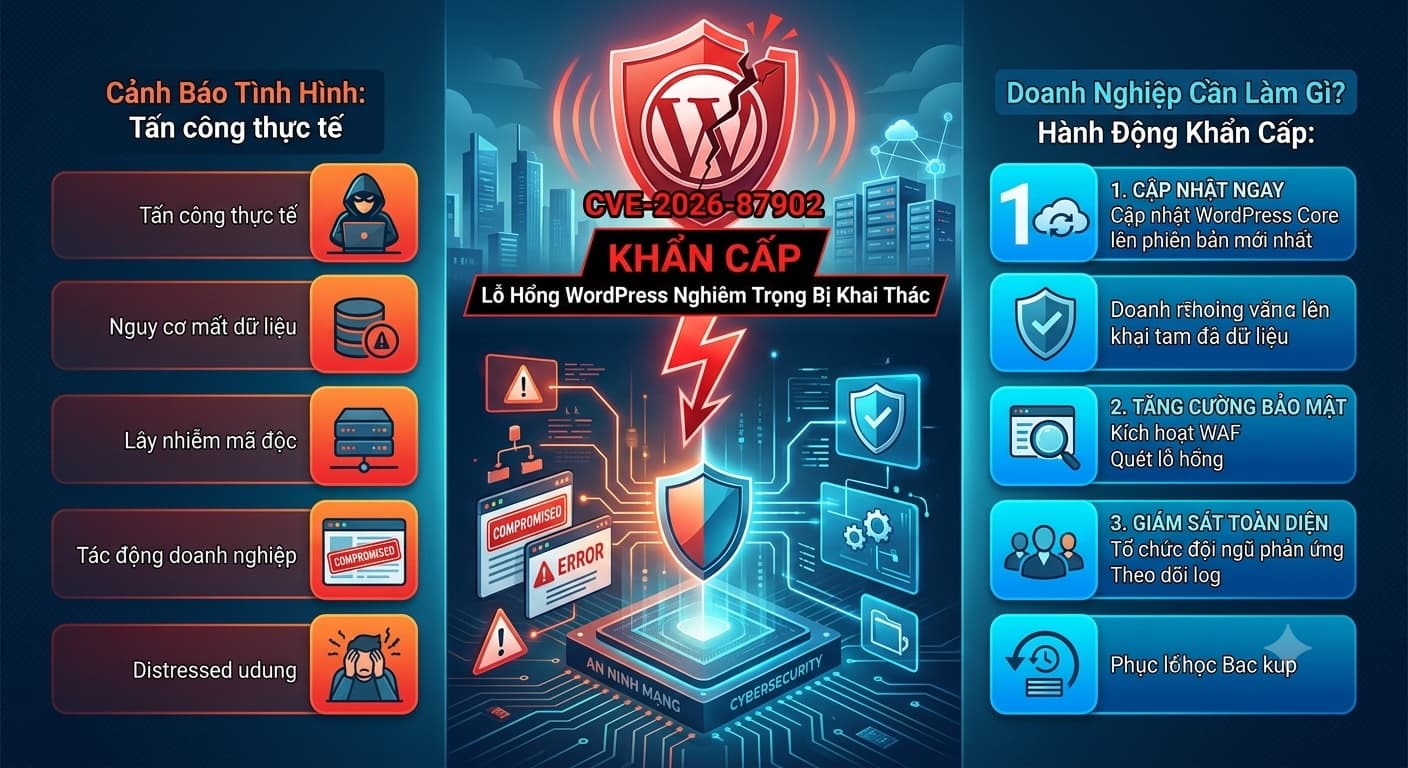
Urgent Alert: Critical WordPress Core Vulnerability CVE-2026-87902 Under Active Exploitation – What Businesses Need to Do
WordPress has released an emergency security update for CVE-2026-87902 (CVSS 9.2). Attackers are actively exploiting this flaw to compromise websites. Update now.
Urgent Alert: Critical WooCommerce Plugin Flaw Actively Exploited to Deploy PHP Web Shells
CVE-2026-27540 in WooCommerce Wholesale Lead Capture is under active exploit. Attackers are uploading PHP backdoors. Update to 2.0.3.2 immediately.
Urgent Security Alert: Critical Elementor Pro Vulnerability Actively Exploited – Over 6 Million WordPress Sites at Risk
A critical unauthenticated file upload vulnerability (CVE-2026-32475) in Elementor Pro is being actively exploited in the wild. Update immediately to secure your site!
Urgent Alert: Critical miniOrange SAML SSO Vulnerabilities Under Active Exploitation on WordPress
Security alert for businesses running WordPress with miniOrange SAML 2.0 SSO plugin. Attackers are actively exploiting flaws to bypass authentication.
Urgent Security Alert: Critical Forminator Forms Vulnerability Poses RCE Risk to Over 600,000 WordPress Sites
The critical WordPress security vulnerability CVE-2026-15748 (CVSS 9.8) in the Forminator Forms plugin allows unauthenticated remote attackers to compromise business websites.
Emergency Alert: wp2shell Pre-Auth RCE in WordPress Core Demands Immediate Action
The wp2shell vulnerability chain (CVE-2026-63030 & CVE-2026-60137) allows unauthenticated RCE on default WordPress installs. Learn how to secure your business site now.